For Canadian P&C insurance brokerages · independent & MGA

Technology and cyber leadership built for insurance brokerages

Your brokerage holds client personal information, banking details and carrier portal access, usually with a small team, one broker management system and an MSP ticket queue. ABISOL provides senior technology and cybersecurity leadership that protects your clients, your carrier relationships and your E&O standing, without a full-time executive.

  • Insurance-sector experience
  • CISSP · CISM · PMP · MBA
  • Vendor-independent
The pressures you face

The technology and cyber pressures on insurance brokerages

Brokerages hold data a bank would protect carefully, with the staffing of a small business.

  • Regulator expectations
    In Ontario, RIBO recommends every brokerage adopt a written cyber security program and report incidents to consumers, RIBO and its insurer.
  • Carrier and cyber-insurer requirements
    Insurers increasingly ask for proof of cyber liability coverage and controls such as multi-factor authentication.
  • Sensitive client data
    Personal information, dates of birth, banking details and policy history, plus the credentials to carrier portals.
  • Payment and wire fraud
    Email impersonation targets premium payments, commissions and changes to banking details.
  • A small team wearing every hat
    Producers and CSRs on laptops and personal phones, often working remotely, with no one senior overseeing security.
  • One BMS, one email tenant, one MSP
    Critical operations concentrated in a few systems and providers, with limited oversight of each.
  • Growth and consolidation
    Acquisitions and book transfers mean integrating systems, data, staff and security, often quickly.
60%

of Coalition's 2024 cyber-insurance claims started with business email compromise or funds-transfer fraud.

Source: Coalition 2025 Cyber Claims Report (2024 claims)
CA$7.11M

average cost of a data breach for Canadian organizations in 2026, up from CA$6.98M in 2025.

Source: IBM Cost of a Data Breach Report 2026, as reported by BNN Bloomberg

Regulatory context: RIBO's Principal Broker Handbook guidance on cyber security recommends a written cyber security program covering data, safeguards, risks and incident reporting. It also recommends MFA for all employees and cyber liability insurance, and notes that RIBO intends to consult on whether cyber insurance should be mandatory for registered firms. Brokers outside Ontario answer to their own provincial regulator, and CISRO's Cybersecurity Readiness tool for insurance intermediaries applies across Canada. Read our guide to what RIBO expects, with a 28-point checklist.

Why the usual approach falls short

Why brokerage IT stays reactive, even with a good MSP

  • The MSP runs operations, not strategy

    Devices get patched and tickets closed, but nobody owns cyber risk or the brokerage's technology direction.

  • Nobody senior has the time

    The Principal Broker and owners are running the business; technology decisions wait.

  • Controls exist but aren't documented

    Hard to prove to RIBO, carriers or an underwriter what is actually in place.

  • Systems don't talk to each other

    BMS, email, accounting and carrier portals linked by people re-keying data.

  • Cyber is treated as a technical issue

    Instead of a business risk to clients, carrier appointments and E&O.

How ABISOL helps

Fractional CIO and CISO leadership for your brokerage, working alongside your MSP

ABISOL works alongside your people, MSP and vendors. We provide executive direction, governance and advocacy, and we don't replace anyone. Lead the IT team? See how we work with you.

  1. Assess

    Cyber posture checked against RIBO's recommended program elements and typical insurer requirements, plus a BMS and vendor review.

  2. Advise

    A Fractional CIO and CISO for the Principal Broker and owners, with a 12-month technology and cyber roadmap.

  3. Transform

    BMS, Microsoft 365 and accounting working as one system of record. Repetitive work automated, with practical AI rules for staff.

  4. Deliver

    BMS selection or migration, acquisition integration and vendor negotiation.

  5. Govern

    A written cyber program, an incident plan with RIBO, insurer and client notification steps, payment controls and vendor oversight.

Proof, not promises

Experience and artifacts your owners and carriers can rely on

Regional insurer

Claims intake that no longer depends on manual sorting

Problem
Staff spent over 1,000 hours a month manually routing claims that arrived by email.
ABISOL action
Designed and delivered an AI classification and routing flow on the insurer's existing Microsoft 365 licensing.
Result
40% reduction in manual claims routing, with no new platform purchase.
What you walk away with

  • Cyber risk register, ranked for the owners
  • One-page cyber dashboard for the Principal Broker
  • Written cyber security policies and procedures manual
  • Cyber-insurance and regulatory evidence file
  • 12-month technology and cyber roadmap
  • Incident response playbook with notification steps
  • MSP and vendor scorecard with renewal dates
  • Carrier and insurer readiness plan

Yours to keep, whether or not you continue.

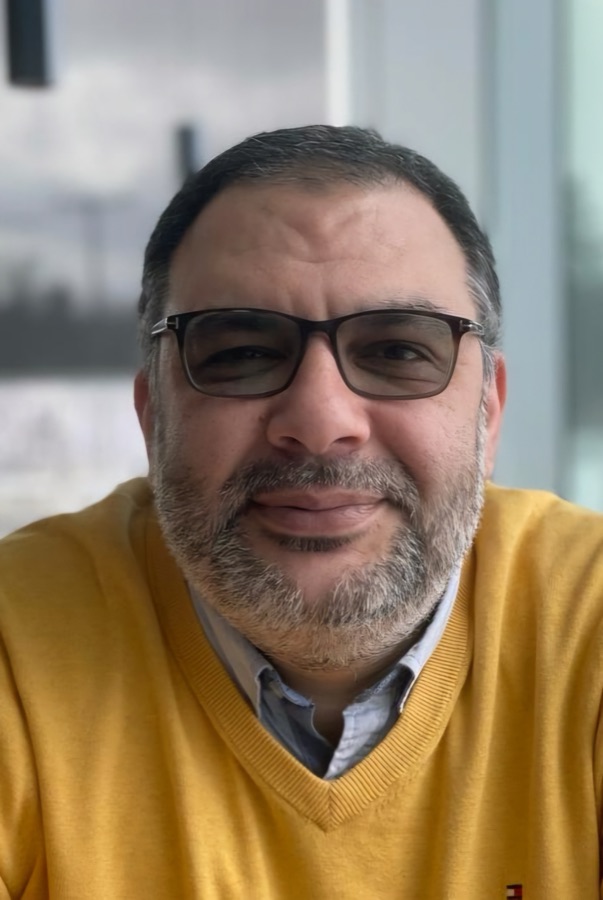
Mohammad Elmallah

Mohammad Elmallah

Fractional CIO, CTO & CISO · CISSP · CISM · PMP · MBA

Mohammad has led technology in the insurance sector and has built cybersecurity programs from policy through to executive and Board reporting. He holds the CISSP and CISM security credentials.

More about Mohammad
Low-risk first step

Start with a complimentary Technology & Cyber Health Check

A focused conversation with your Principal Broker and operations lead, so you can decide based on facts.

  • 45–60 minutes with your Principal Broker and operations lead
  • A one-page summary you keep
  • No retainer, no commitment
Request the Health Check
Straight answers

Questions insurance brokerages ask us

We already pay an MSP. Do we replace them?

No. They do different jobs. Keep a good MSP for the ticket queue. ABISOL governs above it, sets the strategy and holds the provider to clear service levels.

Aren't we too small to be a target?

Attacks are automated, and brokerages hold valuable client data and handle real funds. Email impersonation and payment fraud in particular don't depend on an organization's size.

Is RIBO's cyber guidance mandatory?

RIBO's Principal Broker Handbook guidance recommends a written cyber security program, MFA and cyber liability insurance, and RIBO has said it intends to consult on whether cyber insurance should be mandatory. Either way, carriers and cyber insurers increasingly expect these controls.

Will this help our cyber-insurance renewal?

We help you put the controls insurers commonly ask about in place and document them, so you can answer underwriting questions accurately and confidently. We don't sell insurance and can't promise premium outcomes.

We can't afford a full-time CIO or CISO.

That's the gap fractional leadership is designed for: senior judgment for an agreed amount of time each month, without an executive salary.

We're not ready for AI.

That's fine. We start with fundamentals: security, data and systems that work together. Then we set practical rules for how producers and staff may use AI tools, before anyone pastes client data into one.

Can we trust an outsider with our data?

We work with least-privilege access, avoid holding your sensitive data wherever possible, and sign an NDA. You keep ownership and control throughout.

Next step

Discuss your brokerage's technology and cyber priorities

A no-obligation conversation about where you stand and what to do first.

Prefer slides? View the presentation version · All services

Book an Executive ConsultationComplimentary 30-minute first conversation